Static Analysis & Code Quality
535 items from analysis-tools-dev/static-analysis ★14,831
-
Coverity synopsys.com
copyright: — Synopsys Coverity supports 20 languages and over 70 frameworks including Ruby on rails, Scala, PHP, Python, JavaScript, TypeScript, Java, Fortran, C, C++, C#, VB.NET.
-
SVF svf-tools.github.io
A static tool that enables scalable and precise interprocedural dependence analysis for C and C++ programs.
-
styler styler.r-lib.org
Formatting of R source code files and pretty-printing of R code.
-
Spectral stoplight.io
A flexible JSON/YAML linter, with out-of-the-box support for OpenAPI v2/v3 and AsyncAPI v2.
-
staticcheck staticcheck.io
Go static analysis that specialises in finding bugs, simplifying code and improving performance.
-
squawk squawkhq.com
Linter for PostgreSQL, focused on migrations. Prevents unexpected downtime caused by database migrations and encourages best practices around Postgres schemas and SQL.
-
SQLFluff sqlfluff.com
Multiple dialect SQL linter and formatter.
-
SpotBugs spotbugs.github.io
SpotBugs is FindBugs' successor. A tool for static analysis to look for bugs in Java code.
-
Spoon spoon.gforge.inria.fr
Spoon is a metaprogramming library to analyze and transform Java source code (incl Java 9, 10, 11, 12, 13, 14). It parses source files to build a well-designed AST with powerful analysis and transformation API. Can be integrated in Maven and Gradle.
-
splint splint.org
Annotation-assisted static program checker.
-
Cobra spinroot.com
copyright: — Structural source code analyzer by NASA's Jet Propulsion Laboratory.
-
CScout spinellis.gr
Complexity and quality metrics for C and C preprocessor code.
-
SourceMeter sourcemeter.com
copyright: — Static Code Analysis for C/C++, Java, C#, Python, and RPG III and RPG IV versions (including free-form).
-
Nagelfar sourceforge.net
A static syntax checker for Tcl.
-
WhiteHat Application Security Platform source.whitehatsec.com
copyright: — WhiteHat Scout (for Developers) combined with WhiteHat Sentinel Source (for Operations) supporting WhiteHat Top 40 and OWASP Top 10.
-
Sorbet sorbet.org
A fast, powerful type checker designed for Ruby.
-
Soot soot-oss.github.io
A framework for analyzing and transforming Java and Android applications.
-
Sonatype sonatype.com
copyright: — Reports known vulnerabilities in common dependencies and recommends updated packages to minimize breaking changes
-
Sigrid softwareimprovementgroup.com
copyright: — Sigrid helps you to improve your software by measuring your system's code quality, and then compares the results against a benchmark of thousands of industry systems to give you concrete advice on areas where you can improve.
-
skillsaw skillsaw.org
Configurable linter for the files that steer AI coding agents, including skills, plugins, instruction files, hooks, and related configuration. Detects structural, content-quality, and security issues and provides deterministic autofixes, baselines, and CI-ready output.
-
Goodcheck sider.github.io
Regexp based customizable linter.
-
shellcheck shellcheck.net
ShellCheck, a static analysis tool that gives warnings and suggestions for bash/sh shell scripts.
-
Semgrep Supply Chain semgrep.dev
copyright: — Quickly find and remediate high-priority security issues. Semgrep Supply Chain prioritizes the 2% of vulnerabilities that are reachable from your code.
-
StaticReviewer securityreviewer.net
copyright: — Static Reviewer executes code checks according to the most relevant Secure Coding Standards, OWASP, CWE, CVE, CVSS, MISRA, CERT, for 40+ programming languages, using 1000+ built-in validation rules for Security, Deadcode & Best Practices Available a module for…
-
Precaution securesauce.dev
Precaution is a static analysis security tool (SAST) designed to find potentially critical vulnerabilities in source code prior to production. It is available as a CLI, GitHub Action, and GitHub App.
-
gosec (gas) securego.io
Inspects source code for security problems by scanning the Go AST.
-
Understand scitools.com
copyright: — Code visualization tool that provides code analysis, standards testing, metrics, graphing, dependency analysis and more for Ada, VHDL, and others.
-
SAST Online sast.online
copyright: — Check the Android Source code thoroughly to uncover and address potential security concerns and vulnerabilities. Static application security testing (Static Code Analysis) tool Online
-
Safety safetycli.com
Python dependency vulnerability scanner designed to enhance software supply chain security by detecting packages with known vulnerabilities. Checks Python dependencies against a database of known security vulnerabilities and provides detailed reports. Supports CI/CD integration…
-
SafeQL safeql.dev
Validate and auto-generate TypeScript types from raw SQL queries in PostgreSQL. SafeQL is an ESLint plugin for writing SQL queries in a type-safe way.
-
cargo-audit rustsec.org
Audit Cargo.lock for crates with security vulnerabilities reported to the RustSec Advisory Database.
-
clippy rust-lang.github.io
A code linter to catch common mistakes and improve your Rust code.
-
rust-analyzer rust-analyzer.github.io
Supports functionality such as 'goto definition', type inference, symbol search, reformatting, and code completion, and enables renaming and refactorings.
-
flog ruby.sadi.st
Flog reports the most tortured code in an easy to read pain report. The higher the score, the more pain the code is in.
-
flay ruby.sadi.st
Flay analyzes code for structural similarities.
-
actionlint rhysd.github.io
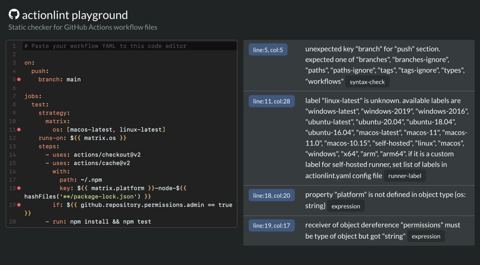
Static checker for GitHub Actions workflow files. Provides an online version.
-
revive revive.run
Fast, configurable, extensible, flexible, and beautiful linter for Go. Drop-in replacement of golint.
-
retire.js retirejs.github.io
Scanner detecting the use of JavaScript libraries with known vulnerabilities.
-
Repowise repowise.dev
Deterministic, zero-LLM code-health analysis. Scores every file 1-10 for defect risk, maintainability, and performance from 25 markers: McCabe complexity, LCOM4 cohesion, god classes, Rabin-Karp clone detection, change entropy, and untested hotspots. Adds a dependency graph…
-
SwiftLint realm.github.io
A tool to enforce Swift style and conventions.
-
rails_best_practices rails-bestpractices.com
A code metric tool for Rails projects
-
Qwiet AI qwiet.ai
copyright: — Identify vulnerabilities that are unique to your code base before they reach production. Leverages the Code Property Graph (CPG) to run its analyses concurrently in a single graph of graphs. Automatically finds business logic flaws in dev like hardcoded secrets and…
-
qulice qulice.com
Combines a few (pre-configured) static analysis tools (checkstyle, PMD, Findbugs, ...).
-
Qualys Container Security qualys.com
copyright: — Container native application protection to provide visibility and control of containerized applications.
-
pyrefly pyrefly.org
A fast, incremental type checker and language server for Python, providing IDE features like code navigation, semantic highlighting, and code completion.
-
Pysa pyre-check.org
A tool based on Facebook's pyre-check to identify potential security issues in Python code identified with taint analysis.
-
pyre-check pyre-check.org
A fast, scalable type checker for large Python codebases. Pyre-check has been superseded by Pyrefly, its next iteration.
-
fprettify pypi.python.org
Auto-formatter for modern fortran source code, written in Python. Fprettify is a tool that provides consistent whitespace, indentation, and delimiter alignment in code, including the ability to change letter case and handle preprocessor directives, all while preserving revision…
-
pyupgrade pypi.org
A tool (and pre-commit hook) to automatically upgrade syntax for newer versions of the language.
-
pyflakes pypi.org
Check Python source files for errors.
- next page of items loading…