Static Analysis & Code Quality
535 items from analysis-tools-dev/static-analysis ★14,831
-
pylint pylint.pycqa.org
Looks for programming errors, helps enforcing a coding standard and sniffs for some code smells. It additionally includes pyreverse (an UML diagram generator) and symilar (a similarities checker).
-
pycodestyle pycodestyle.pycqa.org
(Formerly pep8) Check Python code against some of the style conventions in PEP 8.
-
pyanalyze pyanalyze.readthedocs.io
A tool for programmatically detecting common mistakes in Python code, such as references to undefined variables and type errors. It can be extended to add additional rules and perform checks specific to particular functions.
-
PVS-Studio pvs-studio.com
copyright: — PVS-Studio is a SAST tool that enhances code quality, security, and safety. Supported languages: C, C++, C#, Java, Go, JavaScript and TypeScript. Works on Windows, macOS, Linux. Supports intermodular, incremental, data flow analysis, taint analysis. Provides…
-
Puma Scan pumasecurity.io
Puma Scan provides real time secure code analysis for common vulnerabilities (XSS, SQLi, CSRF, LDAPi, crypto, deserialization, etc.) as development teams write code in Visual Studio.
-
Application Inspector ptsecurity.com
copyright: — Commercial Static Code Analysis which generates exploits to verify vulnerabilities.
-
PT Application Inspector ptsecurity.com
copyright: — Identifies code flaws and detects vulnerabilities to prevent web attacks. Demonstrates remote code execution by presenting possible exploits.
-
Psalm psalm.dev
Static analysis tool for finding type errors in PHP applications.
-
solhint protofire.github.io
Solhint is an open source project created by https://protofire.io. Its goal is to provide a linting utility for Solidity code.
-
Project Wallace CSS Analyzer projectwallace.com
Analytics for CSS, part of Project Wallace.
-
PMD pmd.github.io
A source code analyzer for Java, Salesforce Apex, Javascript, PLSQL, XML, XSL and others.
-
Php Inspections (EA Extended) plugins.jetbrains.com
A Static Code Analyzer for PHP.
-
Cloud (IaC) Security for JetBrains IDEs plugins.jetbrains.com
Cloud (IaC) Security plugin for JetBrains IDEs. Performs real-time inspections of Docker & Kubernetes IaC with 50+ rules based on Docker image/build security best practices, Kubernetes Pod Security Standards, and NSA/CISA Kubernetes Hardening Guidance.
-
Doop plast-lab.github.io
Doop is a declarative framework for static analysis of Java/Android programs, centered on pointer analysis algorithms. Doop provides a large variety of analyses and also the surrounding scaffolding to run an analysis end-to-end (fact generation, processing, statistics, etc.).
-
test pkg.go.dev
Show location of test failures from the stdlib testing module.
-
sh pkg.go.dev
A shell parser, formatter, and interpreter with bash support; includes shfmt
-
gotype pkg.go.dev
Syntactic and semantic analysis similar to the Go compiler.
-
PHPStan phpstan.org
PHP Static Analysis Tool - discover bugs in your code without running it!
-
PhpMetrics phpmetrics.org
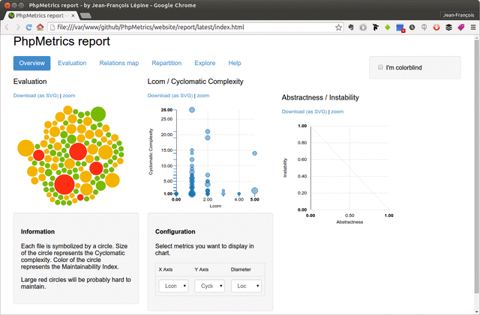
Calculates and visualizes various code quality metrics.
-
PHPMD phpmd.org
Finds possible bugs in your code.
-
phpDocumentor phpdoc.org
Analyzes PHP source code to generate documentation.
-
Phasar phasar.org
A LLVM-based static analysis framework which comes with a taint and type state analysis.
-
perltidy perltidy.sourceforge.net
Perltidy is a Perl script which indents and reformats Perl scripts to make them easier to read. The formatting can be controlled with command line parameters. The default parameter settings approximately follow the suggestions in the Perl Style Guide. Besides reformatting…
-
Klocwork perforce.com
copyright: — Quality and Security Static analysis for C/C++, Java and C#.
-
Helix QAC perforce.com
copyright: — Enterprise-grade static analysis for embedded software. Supports MISRA, CERT, and AUTOSAR coding standards.
-
Pascal Expert peganza.com
copyright: — IDE plugin for code analysis. Includes a subset of Pascal Analyzer reporting capabilities and is available for Delphi versions 2007 and later.
-
pdepend pdepend.org
Calculates software metrics like cyclomatic complexity for PHP code.
-
PC-lint pclintplus.com
copyright: — Static analysis for C/C++. Runs natively under Windows/Linux/MacOS. Analyzes code for virtually any platform, supporting C11/C18 and C++17.
-
parasoft parasoft.com
copyright: — Automated Software Testing Solutions for unit-, API-, and web UI testing. Complies with MISRA, OWASP, and others.
-
elm-review package.elm-lang.org
Analyzes whole Elm projects, with a focus on shareable and custom rules written in Elm that add guarantees the Elm compiler doesn't give you.
-
OWASP Source Code Analysis Tools owasp.org
List of tools maintained by the Open Web Application Security Project
-
OWASP Noir owasp-noir.github.io
Attack surface detector that identifies endpoints by static analysis.
-
Fortify opentext.com
copyright: — A commercial static analysis platform that supports the scanning of C/C++, C#, VB.NET, VB6, ABAP/BSP, ActionScript, Apex, ASP.NET, Classic ASP, VB Script, Cobol, ColdFusion, HTML, Java, JS, JSP, MXML/Flex, Objective-C, PHP, PL/SQL, T-SQL, Python (2.6, 2.7), Ruby…
-
OpenTaint opentaint.org
Open-source taint analysis engine for Java and Kotlin applications, formerly Seqra. Tracks data flow across function boundaries to find security vulnerabilities, with Spring support, YAML rules, and CI integrations.
-
NodeJSScan opensecurity.in
A static security code scanner for Node.js applications powered by libsast and semgrep that builds on the njsscan cli tool. It features a UI with various dashboards about an application's security status.
-
OpenSCAP open-scap.org
Suite of automated audit tools to examine the configuration and known vulnerabilities following the NIST-certified Security Content Automation Protocol (SCAP).
-
Offensive 360 offensive360.com
copyright: — Commercial Static Code Analysis system doesn't require building the source code or pre-compilation.
-
AppChecker npo-echelon.ru
copyright: — Static analysis for C/C++/C#, PHP and Java.
-
DrNim nim-lang.org
DrNim combines the Nim frontend with the Z3 proof engine in order to allow verify / validate software written in Nim.
-
NDepend ndepend.com
copyright: — Measure, query and visualize your code and avoid unexpected issues, technical debt and complexity.
-
MythX mythx.io
copyright: — MythX is an easy to use analysis platform which integrates several analysis methods like fuzzing, symbolic execution and static analysis to find vulnerabilities with high precision. It can be integrated with toolchains like Remix or VSCode or called from the…
-
mypy mypy-lang.org
A static type checker that aims to combine the benefits of duck typing and static typing, frequently used with MonkeyType.
-
MOPSA mopsa.lip6.fr
A static analyzer designed to easily reuse abstract domains across widely different languages (such as C and Python).
-
Mobb mobb.ai
copyright: — Mobb is a trusted, automatic vulnerability fixer that secures applications, reduces security backlogs, and frees developers to focus on innovation. Mobb is free for open-source projects.
-
Griffe mkdocstrings.github.io
Signatures for entire Python programs. Extract the structure, the frame, the skeleton of your project, to generate API documentation or find breaking changes in your API.
-
Perl::Critic metacpan.org
Critique Perl source code for best-practices.
-
Mega-Linter megalinter.io
Mega-Linter can handle any type of project thanks to its 70+ embedded Linters, its advanced reporting, runnable on any CI system or locally, with assisted installation and configuration, able to apply formatting and fixes
-
mdformat mdformat.rtfd.io
CommonMark compliant Markdown formatter
-
Polyspace Code Prover mathworks.com
copyright: — Provide code verification that proves the absence of overflow, divide-by-zero, out-of-bounds array access, and certain other run-time errors in C and C++ source code.
-
Polyspace Bug Finder mathworks.com
copyright: — Identifies run-time errors, concurrency issues, security vulnerabilities, and other defects in C and C++ embedded software.
- next page of items loading…