Static Analysis & Code Quality
535 items from analysis-tools-dev/static-analysis ★14,831
-
DesigniteJava designite-tools.com
copyright: — DesigniteJava supports detection of various architecture, design, and implementation smells along with computation of various code quality metrics.
-
DerScanner derscanner.com
copyright: — Multi-language Static Application Security Testing (SAST) platform that detects critical vulnerabilities, including hardcoded secrets, weak cryptography, backdoors, SQL injections, insecure configurations, etc.
-
axe-core deque.com
Accessibility engine for automated Web UI testing. Tests HTML against WCAG 2.0, 2.1, and 2.2 guidelines. Used by Google Lighthouse, Microsoft Accessibility Insights, and thousands of organizations worldwide.
-
DepWarden depwarden.in
copyright: — Free, anonymous SCA + SAST scanner. SCA: scans npm, PyPI, Maven, Go, Cargo, Ruby, NuGet dependencies for CVEs (OSV/KEV/EPSS), typosquats and supply-chain risk. SAST: pattern + taint analysis for 15 languages, 300+ rules. No account, no source upload. Available as a…
-
DeepSource deepsource.com
copyright: — In-depth static analysis to find issues in verticals of bug risks, security, anti-patterns, performance, documentation and style. Native integrations with GitHub, GitLab and Bitbucket. Less than 5% false positives.
-
DeepScan deepscan.io
copyright: — An analyzer for JavaScript which targets runtime errors and quality issues rather than coding conventions.
-
deal deal.readthedocs.io
Design by contract for Python. Write bug-free code. By adding a few decorators to your code, you get for free tests, static analysis, formal verification, and much more.
-
lacheck ctan.org
A tool for finding common mistakes in LaTeX documents.
-
PHP Coding Standards Fixer cs.symfony.com
Fixes your code according to standards like PSR-1, PSR-2, and the Symfony standard.
-
ameba crystal-ameba.github.io
A static code analysis tool for Crystal.
-
rhabdomancer crates.io
IDA Pro headless plugin that locates calls to potentially insecure API functions in a binary file.
-
cargo-semver-checks crates.io
Scan your Rust crate releases for semver violations. It can be used either directly via the CLI, as a GitHub Action in CI, or via release managers like release-plz. It found semver violations in more than 1 in 6 of the top 1000 most-downloaded crates on crates.io.
-
JBMC cprover.org
Bounded model-checker for Java (bytecode), verifies user-defined assertions, standard assertions, several coverage metric analyses.
-
CBMC cprover.org
Bounded model-checker for C programs, user-defined assertions, standard assertions, several coverage metric analyses.
-
cppcheck cppcheck.sourceforge.io
Static analysis of C/C++ code.
-
cpp-linter-action cpp-linter.github.io
A Github Action for linting C/C++ code integrating clang-tidy and clang-format to collect feedback provided in the form of thread comments and/or annotations.
-
CPAchecker cpachecker.sosy-lab.org
A tool for configurable software verification of C programs. The name CPAchecker was chosen to reflect that the tool is based on the CPA concepts and is used for checking software programs.
-
Corgea corgea.com
copyright: — Corgea is an AI-powered SAST scanner that helps developers find and fix insecure code. It finds business logic flaws, broken authentication, API vulnerabilities, and more with little false positives. Additionally, it automatically writes security fixes for them to…
-
commitlint commitlint.js.org
checks if your commit messages meet the conventional commit format
-
Codiga codiga.io
copyright: — Automated Code Reviews and Technical Debt management platform that supports 12+ languages.
-
CodeSonar from GrammaTech codesecure.com
copyright: — Advanced, whole program, deep path, static analysis of C, C++, Java and C# with easy-to-understand explanations and code and path visualization.
-
CodeScene codescene.com
copyright: — CodeScene is a quality visualization tool for software. Prioritize technical debt, detect delivery risks, and measure organizational aspects. Fully automated.
-
CodeScan codescan.io
copyright: — Code Quality and Security for Salesforce Developers. Made exclusively for the Salesforce platform, CodeScan’s code analysis solutions provide you with total visibility into your code health.
-
CodeQue codeque.co
Ecosystem for structural matching JavaScript and TypeScript code. Offers search tool that understands code structure. Available as CLI tool and Visual Studio Code extension. It helps to search code faster and more accurately making you workflow more effective. Soon it will…
-
Code Pathfinder codepathfinder.dev
Opensource Static Code Analysis for security teams with Inter file dataflow taint analysis. Built for finding vulnerabilities, advanced structural search, derive insights and supports MCP server.
-
CodeNarc codenarc.github.io
A static analysis tool for Groovy source code, enabling monitoring and enforcement of many coding standards and best practices.
-
codechecker codechecker.readthedocs.io
A defect database and viewer extension for the Clang Static Analyzer with web GUI.
-
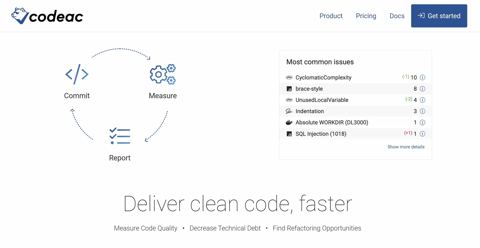
Codeac codeac.io
copyright: — Automated code review tool integrates with GitHub, Bitbucket and GitLab (even self-hosted). Available for JavaScript, TypeScript, Python, Ruby, Go, PHP, Java, Docker, and more. (open-source free)
-
Code Intelligence code-intelligence.com
copyright: — CI/CD-agnostic DevSecOps platform which combines industry-leading fuzzing engines for finding bugs and visualizing code coverage
-
Code-Graph-RAG code-graph-rag.com
Builds knowledge graphs from multi-language codebases using Tree-sitter AST parsing and stores them in Memgraph. Supports 11 programming languages with a unified graph schema and enables natural language querying and editing of code structure and relationships. Functions as an…
-
clang-tidy clang.llvm.org
Clang-based C++ linter tool with the (limited) ability to fix issues, too.
-
scan-build clang-analyzer.llvm.org
Frontend to drive the Clang Static Analyzer built into Clang via a regular build.
-
checkstyle checkstyle.org
Checking Java source code for adherence to a Code Standard or set of validation rules (best practices).
-
Checkmarx CxSAST checkmarx.com
copyright: — Commercial Static Code Analysis which doesn't require pre-compilation.
-
Checker Framework checkerframework.org
Pluggable type-checking for Java. This is not just a bug-finder, but a verification tool that gives a guarantee of correctness. It comes with 27 pre-built type systems, and it enables users to define their own type system; the manual lists over 30 user-contributed type systems.
-
Frink catless.ncl.ac.uk
A Tcl formatting and static check program (can prettify the program, minimise, obfuscate or just sanity check it).
-
CAST Highlight castsoftware.com
copyright: — Commercial Static Code Analysis which runs locally, but uploads the results to its cloud for presentation.
-
C2Rust c2rust.com
C2Rust helps you migrate C99-compliant code to Rust. The translator (or transpiler) produces unsafe Rust code that closely mirrors the input C code.
-
buf buf.build
Provides a CLI linter that enforces good API design choices and structure
-
brakeman brakemanscanner.org
A static analysis security vulnerability scanner for Ruby on Rails applications.
-
dylint blog.trailofbits.com
A tool for running Rust lints from dynamic libraries. Dylint makes it easy for developers to maintain their own personal lint collections.
-
Black Duck blackducksoftware.com
copyright: — Tool to analyze source code and binaries for reusable code, necessary licenses and potential security aspects.
-
Black black.readthedocs.io
The uncompromising Python code formatter.
-
biome biomejs.dev
A toolchain for web projects, aimed to provide functionalities to maintain them. Biome formats and lints code in a fraction of a second. It is the successor to Rome. It is designed to eventually replace Biome is designed to eventually replace Babel, ESLint, webpack, Prettier…
-
bandit bandit.readthedocs.io
A tool to find common security issues in Python code.
-
Axivion Bauhaus Suite axivion.com
copyright: — Tracks down error-prone code locations, style violations, cloned or dead code, cyclic dependencies and more for C/C++, C#/.NET, Java and Ada 83/Ada 95.
-
WAP awap.sourceforge.net
Tool to detect and correct input validation vulnerabilities in PHP (4.0 or higher) web applications and predicts false positives by combining static analysis and data mining.
-
ruff astral.sh
Fast Python linter, written in Rust. 10-100x faster than existing linters. Compatible with Python 3.10. Supports file watcher.
-
AST Metrics ast-metrics.dev
Multi-language maintainability analyzer. Computes cyclomatic and cognitive complexity, Halstead volume, afferent/efferent coupling and maintainability index, detects communities in the dependency graph, and generates an explorable HTML report plus JSON, Markdown, SARIF and…
-
ast-grep ast-grep.github.io
ast-grep is a powerful tool designed for managing code at scale using Abstract Syntax Trees (AST). Think of it as a hybrid of grep, eslint, and codemod, with the ability to search, lint, and rewrite code based on its structure rather than plain text. It supports multiple…
- next page of items loading…