PCAPTools
118 items from caesar0301/awesome-pcaptools ★3,431
-
Zeek zeek.org
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
-
-
Suricata suricata-ids.org
Suricata is a high performance Network IDS, IPS and Network Security Monitoring engine. Open Source and owned by a community run non-profit foundation, the Open Information Security Foundation (OISF). Suricata is developed by the OISF and its supporting vendors.
-
Snort snort.org
Snort is a free and open source network intrusion prevention system (NIPS) and network intrusion detection system (NIDS)created by Martin Roesch in 1998. Snort is now developed by Sourcefire, of which Roesch is the founder and CTO. In 2009, Snort entered InfoWorld's Open Source…
-
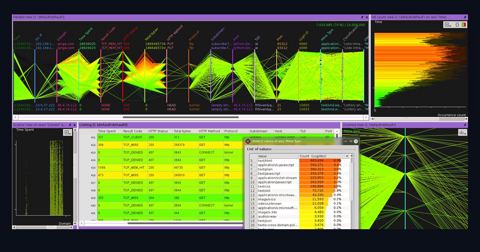
Squey squey.org
Interactive visualization software designed to explore large PCAPs to detect anomalies / weak signals.
-
tcpxtract tcpxtract.sourceforge.net
is a tool for extracting files from network traffic based on file signatures. Extracting files based on file type headers and footers (sometimes called "carving") is an age old data recovery technique.
-
tcpick tcpick.sourceforge.net
is a textmode sniffer libpcap-based that can track, reassemble and reorder tcp streams. Tcpick is able to save the captured flows in different files or displays them in the terminal, and so it is useful to sniff files that are transmitted via ftp or http. It can display all the…
-
-
ntopng ntop.org
Ntopng is a network traffic probe that shows the network usage, similar to what the popular top Unix command does.
-
PF_RING ntop.org
PF_RING is a new type of network socket that dramatically improves the packet capture speed.
-
-
AIEngine bitbucket.org
AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua packet inspection engine with capabilities of learning without any human intervention, NIDS(Network Intrusion Detection System) functionality, DNS domain classification, network collector, network…
-
Xplot xplot.org
The program xplot was written in the late 1980s to support the analysis of TCP packet traces.
-
Xplico xplico.org
The goal of Xplico is extract from an internet traffic capture the applications data contained. For example, from a pcap file Xplico extracts each email (POP, IMAP, and SMTP protocols), all HTTP contents, each VoIP call (SIP), FTP, TFTP, and so on. Xplico isn't a network…
-
TTT www2.sonycsl.co.jp
(Tele Traffic Tapper) is yet another descendant of tcpdump but it is capable of real-time, graphical, and remote traffic-monitoring. ttt won't replace tcpdump, rather, it helps you find out what to look into with tcpdump. ttt monitors the network and automatically picks up the…
-
WireEdit wireedit.com
WireEdit is a free desktop WYSIWYG editor for network packets. It allows editing any stack layer as "rich text" without having any knowledge of packets syntax and encoding rules. The input and output file format is Pcap.
-
-
-
Wireshark suit wiki.wireshark.org
The well-known tool suit to support packet analyzer and protocol decoder. It also includes a few practical tools and scripts to support most of the common usage.
-
Screenshot wiki.ipfire.org
-
Sanitize web.archive.org
Sanitize is a collection of five Bourne shell scripts for reducing tcpdump traces in order to address security and privacy concerns, by renumbering hosts and stripping out packet contents. Each script takes as input a tcpdump trace file and generates to stdout a reduced, ASCII…
-
ITA web.archive.org
The Internet Traffic Archive is a moderated repository to support widespread access to traces of Internet network traffic, sponsored by ACM SIGCOMM. The traces can be used to study network dynamics, usage characteristics, and growth patterns, as well as providing the grist for…
-
ECap web.archive.org
(External Capture) is a distributed network sniffer with a web front- end. Ecap was written many years ago in 2005, but a post on the tcpdump-workers mailing list requested a similar application... so here it is. It would be fun to update it and work on it again if there's any…
-
Multitail vanheusden.com
now has a colorscheme included for monitoring the tcpdump output. It can also filter, convert timestamps to timestrings and much more.
-
Tstat tstat.tlc.polito.it
A passive sniffer able to provide several insight on the traffic patterns at both the network and transport levels with a tremendous set of flow features.
-
TraceWrangler tracewrangler.com
TraceWrangler is a network capture file toolkit running on Windows (or on Linux, using WINE) that supports PCAP as well as the new PCAPng file format, which is now the standard file format used by Wireshark. The most prominent use case for TraceWrangler is the easy sanitization…
-
Yaf tools.netsa.cert.org
It's a reliable piece of software, quite solid and able to generate flow records from pcap. This is very nice for indexing huge pcap or even doing packet capture. The recent version can even extract payloads and put in the flow records.
-
SiLK tools.netsa.cert.org
SiLK (the System for Internet-Level Knowledge), is a collection of traffic analysis tools developed to facilitate security analysis of large networks. The SiLK tool suite supports the efficient collection, storage, and analysis of network flow data.
-
-
Screenshot tecmint.com
- next page of items loading…