Incident Response
218 items from meirwah/awesome-incident-response ★9,444
-
Metadefender Cloud metadefender.com
Free threat intelligence platform providing multiscanning, data sanitization and vulnerability assessment of files.
-
Introduction to DFIR medium.com
By Scott J. Roberts.
-
Cyphon medevel.com
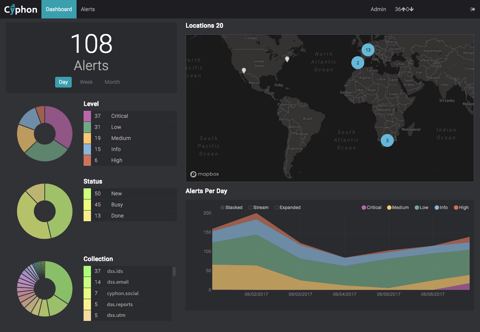
Cyphon eliminates the headaches of incident management by streamlining a multitude of related tasks through a single platform. It receives, processes and triages events to provide an all-encompassing solution for your analytic workflow — aggregating data, bundling and…
-
MAGNET DumpIt magnetforensics.com
Fast memory acquisition tool for Windows (x86, x64, ARM64). Generate full memory crash dumps of Windows machines.
-
Magnet ACQUIRE magnetforensics.com
ACQUIRE by Magnet Forensics allows various types of disk acquisitions to be performed on Windows, Linux, and OS X as well as mobile operating systems.
-
Magnet RAM Capture magnetforensics.com
Free imaging tool designed to capture the physical memory of a suspect’s computer. Supports recent versions of Windows.
-
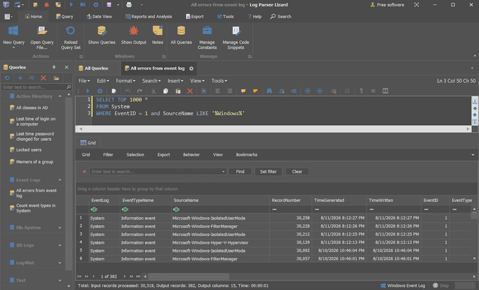
Log Parser Lizard lizard-labs.com
Execute SQL queries against structured log data: server logs, Windows Events, file system, Active Directory, log4net logs, comma/tab separated text, XML or JSON files. Also provides a GUI to Microsoft LogParser 2.2 with powerful UI elements: syntax editor, data grid, chart…
-
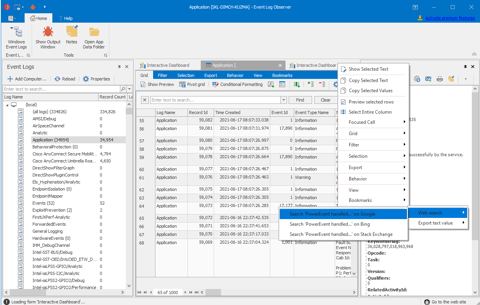
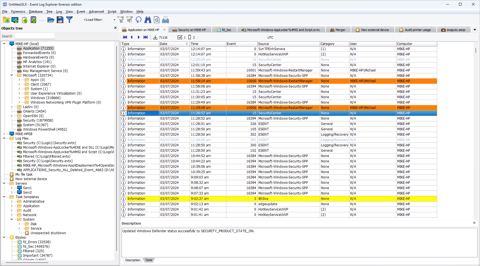
Event Log Observer lizard-labs.com
View, analyze and monitor events recorded in Microsoft Windows event logs with this GUI tool.
-
Limacharlie limacharlie.io
Endpoint security platform composed of a collection of small projects all working together that gives you a cross-platform (Windows, OSX, Linux, Android and iOS) low-level environment for managing and pushing additional modules into memory to extend its functionality.
-
KAPE kroll.com
Kroll Artifact Parser and Extractor (KAPE) by Eric Zimmerman. A triage tool that finds the most prevalent digital artifacts and then parses them quickly. Great and thorough when time is of the essence.
-
Joe Sandbox (Community) joesandbox.com
Joe Sandbox detects and analyzes potential malicious files and URLs on Windows, Android, Mac OS, Linux, and iOS for suspicious activities; providing comprehensive and detailed analysis reports.
-
IPASIS ipasis.com
Real-time IP reputation and email validation API for investigating suspicious interactions. Returns an Interaction Trust Score (0-100) combining VPN/proxy/Tor detection with email risk assessment in a single API call.
-
Guymager guymager.sourceforge.net
Free forensic imager for media acquisition on Linux.
-
Counteractive Playbooks github.com
Counteractive PLaybooks collection.
-
AWS Incident Response Runbook Samples github.com
AWS IR Runbook Samples meant to be customized per each entity using them. The three samples are: "DoS or DDoS attack", "credential leakage", and "unintended access to an Amazon S3 bucket".
-
The Appliance for Digital Investigation and Analysis (ADIA) forensics.cert.org
VMware-based appliance used for digital investigation and acquisition and is built entirely from public domain software. Among the tools contained in ADIA are Autopsy, the Sleuth Kit, the Digital Forensics Framework, log2timeline, Xplico, and Wireshark. Most of the system…
-
GetData Forensic Imager forensicimager.com
Windows based program that will acquire, convert, or verify a forensic image in one of the following common forensic file formats.
-
Memoryze fireeye.com
Free memory forensic software that helps incident responders find evil in live memory. Memoryze can acquire and/or analyze memory images, and on live systems, can include the paging file in its analysis.
-
IOC Finder fireeye.com
Free tool from Mandiant for collecting host system data and reporting the presence of Indicators of Compromise (IOCs). Support for Windows only. No longer maintained. Only fully supported up to Windows 7 / Windows Server 2008 R2.
-
Highlighter fireeye.com
Free Tool available from Fire/Mandiant that will depict log/text file that can highlight areas on the graphic, that corresponded to a key word or phrase. Good for time lining an infection and what was done post compromise.
-
Event Log Explorer eventlogxp.com
Tool developed to quickly analyze log files and other data.
-
Eric Zimmerman Tools ericzimmerman.github.io
An updated list of forensic tools created by Eric Zimmerman, an instructor for SANS institute.
-
Microsoft ProcDump docs.microsoft.com
Dumps any running Win32 processes memory image on the fly.
-
Digital Forensics Discord Server discordapp.com
Community of 8,000+ working professionals from Law Enforcement, Private Sector, and Forensic Vendors. Additionally, plenty of students and hobbyists! Guide here.
-
SANS Investigative Forensic Toolkit (SIFT) Workstation digital-forensics.sans.org
Demonstrates that advanced incident response capabilities and deep dive digital forensic techniques to intrusions can be accomplished using cutting-edge open-source tools that are freely available and frequently updated.
-
Slack DFIR channel dfircommunity.slack.com
Slack DFIR Communitiy channel - Signup here.
-
DFIR ORC dfir-orc.github.io
DFIR ORC is a collection of specialized tools dedicated to reliably parse and collect critical artifacts such as the MFT, registry hives or event logs. DFIR ORC collects data, but does not analyze it: it is not meant to triage machines. It provides a forensically relevant…
-
Cyber Triage cybertriage.com
Cyber Triage collects and analyzes host data to determine if it is compromised. It's scoring system and recommendation engine allow you to quickly focus on the important artifacts. It can import data from its collection tool, disk images, and other collectors (such as KAPE). It…
-
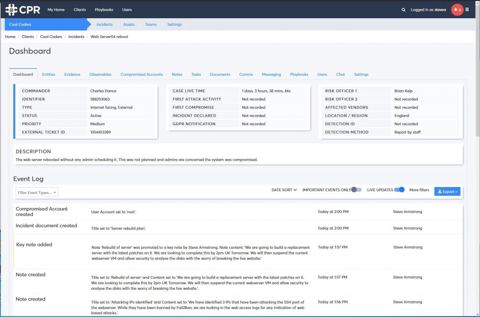
CyberCPR cybercpr.com
Community and commercial incident management tool with Need-to-Know built in to support GDPR compliance while handling sensitive incidents.
-
Crowd Response crowdstrike.com
Lightweight Windows console application designed to aid in the gathering of system information for incident response and security engagements. It features numerous modules and output formats.
-
Computer Aided Investigative Environment (CAINE) caine-live.net
Contains numerous tools that help investigators during their analysis, including forensic evidence collection.
-
Live Response Collection brimorlabs.com
Automated tool that collects volatile data from Windows, OSX, and *nix based operating systems.
-
IREC binalyze.com
All-in-one IR Evidence Collector which captures RAM Image, $MFT, EventLogs, WMI Scripts, Registry Hives, System Restore Points and much more. It is FREE, lightning fast and easy to use.
-
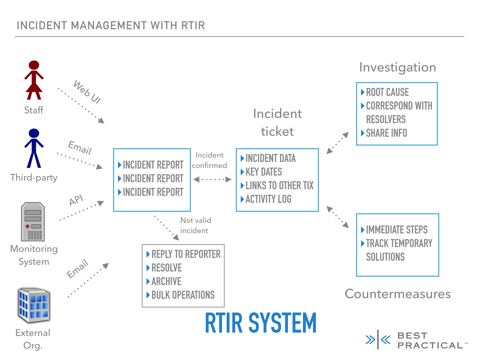
RTIR bestpractical.com
Request Tracker for Incident Response (RTIR) is the premier open source incident handling system targeted for computer security teams. We worked with over a dozen CERT and CSIRT teams around the world to help you handle the ever-increasing volume of incident reports. RTIR…
-
Belkasoft Live RAM Capturer belkasoft.com
Tiny free forensic tool to reliably extract the entire content of the computer’s volatile memory – even if protected by an active anti-debugging or anti-dumping system.
-
Belkasoft Evidence Center belkasoft.com
The toolkit will quickly extract digital evidence from multiple sources by analyzing hard drives, drive images, memory dumps, iOS, Blackberry and Android backups, UFED, JTAG and chip-off dumps.
-
Threat.Zone app.threat.zone
Cloud based threat analysis platform which include sandbox, CDR and interactive analysis for researchers.
-
The Practice of Network Security Monitoring: Understanding Incident Detection and Response amazon.com
Richard Bejtlich's book on IR.
-
Practical Memory Forensics amazon.com
The definitive guide to practice memory forensics. By Svetlana Ostrovskaya and Oleg Skulkin.
-
Operator Handbook: Red Team + OSINT + Blue Team Reference amazon.com
Great reference for incident responders.
-
Intelligence-Driven Incident Response amazon.com
By Scott J. Roberts, Rebekah Brown.
-
Incident Response with Threat Intelligence amazon.com
Great reference to build an incident response plan based also on Threat Intelligence. By Roberto Martinez.
-
Incident Response Techniques for Ransomware Attacks amazon.com
A great guide to build an incident response strategy for ransomware attacks. By Oleg Skulkin.
-
Incident Response & Computer Forensics, Third Edition amazon.com
The definitive guide to incident response.
-
by Gerard Johansen.
-
Crafting the InfoSec Playbook: Security Monitoring and Incident Response Master Plan amazon.com
by Jeff Bollinger, Brandon Enright and Matthew Valites.
-
Art of Memory Forensics amazon.com
Detecting Malware and Threats in Windows, Linux, and Mac Memory.
-
Applied Incident Response amazon.com
Steve Anson's book on Incident Response.
-
AccessData FTK Imager accessdata.com
Forensics tool whose main purpose is to preview recoverable data from a disk of any kind. FTK Imager can also acquire live memory and paging file on 32bit and 64bit systems.