Executable Packing
759 items from dhondta/awesome-executable-packing ★1,628
-
Toward generic unpacking techniques for malware analysis with quantification of code revelation researchgate.net
(August 2009)
-
Deobfuscation of packed and virtualization-obfuscation protected binaries repository.arizona.edu
(June 2011)
-
Unpacking framework for packed malicious executables repositorio-aberto.up.pt
(July 2013)
-
Robust static analysis of portable executable malware repo.zenk-security.com
(December 2014)
-
Executable and linking format (ELF) specification refspecs.linuxfoundation.org
-
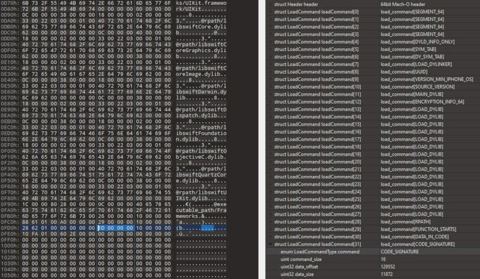
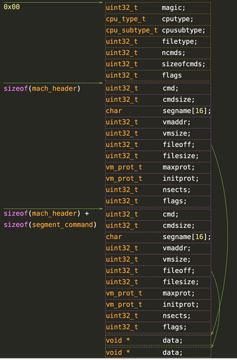
Mach-O - A look at apple executable files redmaple.tech
-
PackHero: A scalable graph-based approach for efficient packer identification re.public.polimi.it
(July 2025) :star:
-
ProTools protools.narod.ru
Programmer's Tools, a web site dedicated for all kinds of tools and utilities for the true WinBloze programmer, including packers, crypters, etc.
-
CryptExec phrack.org
Next-generation runtime binary encryption using on-demand function extraction.
-
-
Anti-unpacker tricks pferrie.tripod.com
-
Standards and policies on packer use pferrie.epizy.com
-
The "Ultimate" anti-debugging reference pferrie.epizy.com
-
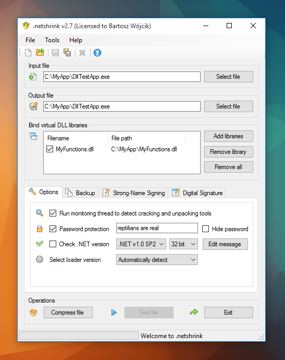
.netshrink pelock.com
Executable compressor for your Windows or Linux .NET application executable file using LZMA.
-
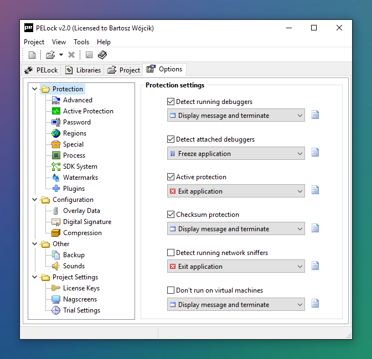
PELock pelock.com
Software protection system for Windows executable files ; protects your applications from tampering and reverse engineering, and provides extensive support for software license key management, including support for time trial periods.
-
PEdump pedump.me
Dump windows PE files using Ruby.
-
PCjs pcjs.org
Uses JavaScript to recreate the IBM PC experience, using original ROMs, CPUs running at their original speeds, and early IBM video cards and monitors.
-
Shiva packetstormsecurity.com
Tool to encrypt ELF executables under Linux.
-
cryptelf packetstormsecurity.com
Modifies binary by appending code to handle runtime decryption, changing the program EP and changing the .note segment to LOAD ; encrypts the .text section by XORing its bytes with a key.
-
BurnEye packetstormsecurity.com
ELF encryption program, x86-linux binary.
-
-
-
Themida oreans.com
From Renovo paper: Themida converts the original x86 instructions into virtual instructions in its own randomized instruction set, and then interpret these virtual instructions at run-time.
-
Code Virtualizer oreans.com
Powerful code obfuscation system for Windows, Linux and macOS applications that helps developers to protect their sensitive code areas against Reverse Engineering with very strong obfuscation code, based on code virtualization.
-
UnThemida: Commercial obfuscation technique analysis with a fully obfuscated program onlinelibrary.wiley.com
(July 2018) :star:
-
Improving malware detection using multi-view ensemble learning onlinelibrary.wiley.com
(August 2016) :star:
-
Packer identification method based on byte sequences onlinelibrary.wiley.com
(November 2018)
-
All-in-one framework for detection, unpacking, and verification for malware analysis onlinelibrary.wiley.com
(January 2019) :star:
-
Classification of malware by using structural entropy on convolutional neural networks ojs.aaai.org
(April 2018)
-
Obsidium obsidium.de
Feature-rich professional software protection and licensing system designed as a cost effective and easy to implement, yet reliable and non-invasive way to protect your 32- and 64-bit Windows software applications and games from reverse engineering.
-
CFF Explorer ntcore.com
PE32/64 and .NET editor, part of the Explorer Suite.
-
PE Detective ntcore.com
This GUI tool can scan single PE files or entire directories (also recursevely) and generate complete reports.
-
NSPack nspack.apponic.com
32/64-bits exe, dll, ocx, scr Windows program compressor.
-
When malware is packin' heat; limits of machine learning classifiers based on static analysis features ndss-symposium.org
(January 2020) :star: :star:
-
Prevalence and impact of low-entropy packing schemes in the malware ecosystem ndss-symposium.org
(February 2020) :star:
-
Things you may not know about Android (Un) packers: A systematic study based on whole-system emulation. ndss-symposium.org
(February 2018)
-
Entropy and the distinctive signs of packer PE files n10info.blogspot.com
-
-
Unpacking the potential of "Packing box" medium.com
-
TitanMist: Your first step to reversing nirvana media.blackhat.com
-
An improved method for packed malware detection using PE header and section table information mecs-press.org
(September 2019)
-
Identifying malware packers through multilayer feature engineering in static analysis mdpi.com
(February 2024) :star:
-
Bypassing heaven’s gate technique using black-box testing mdpi.com
(November 2023) :star:
-
Mimicking anti-viruses with machine learning and entropy profiles mdpi.com
(2019-05-21)
-
Packer detection for multi-layer executables using entropy analysis mdpi.com
(March 2017) :star:
-
Packed malware variants detection using deep belief networks matec-conferences.org
(March 2020)
-
MRC mandiant-red-curtain.apponic.com
(Mandiant Red Curtain) Free software for Incident Responders that assists with the analysis of malware ; it examines executable files (e.g., .exe, .dll, and so on) to determine how suspicious they are based on a set of criteria.
-
MalwareTips malwaretips.com
Community-driven platform providing the latest information and resources on malware and cyber threats.
-
MalwareGallery malwaregallery.com
Yet another malware collection in the Internet.
-
Parsing mach-O files lowlevelbits.org
- next page of items loading…