Executable Packing
759 items from dhondta/awesome-executable-packing ★1,628
-
Design and performance evaluation of binary code packing for protecting embedded software against reverse engineering ieeexplore.ieee.org
(May 2010)
-
A fast flowgraph based classification system for packed and polymorphic malware on the endhost ieeexplore.ieee.org
(April 2010)
-
Program obfuscation by strong cryptography ieeexplore.ieee.org
(February 2010)
-
Packed PE file detection for malware forensics ieeexplore.ieee.org
(December 2009)
-
A unpacking and reconstruction system-agunpacker ieeexplore.ieee.org
(January 2009)
-
Automatic static unpacking of malware binaries ieeexplore.ieee.org
(October 2009)
-
Research and implementation of compression shell unpacking technology for PE file ieeexplore.ieee.org
(May 2009)
-
A heuristic approach for detection of obfuscated malware ieeexplore.ieee.org
(June 2009)
-
Generic unpacking techniques ieeexplore.ieee.org
(February 2009)
-
McBoost: Boosting scalability in malware collection and analysis using statistical classification of executables ieeexplore.ieee.org
(December 2008)
-
PE file header analysis-based packed PE file detection technique (PHAD) ieeexplore.ieee.org
(October 2008)
-
Revealing packed malware ieeexplore.ieee.org
(September 2008)
-
OmniUnpack: Fast, generic, and safe unpacking of malware ieeexplore.ieee.org
(December 2007)
-
Limits of static analysis for malware detection ieeexplore.ieee.org
(December 2007)
-
MetaAware: Identifying metamorphic malware ieeexplore.ieee.org
(December 2007)
-
Software protection through anti-debugging ieeexplore.ieee.org
(May 2007)
-
Detecting obfuscated viruses using cosine similarity analysis ieeexplore.ieee.org
(March 2007)
-
Using entropy analysis to find encrypted and packed malware ieeexplore.ieee.org
(March 2007)
-
PolyUnpack: Automating the hidden-code extraction of unpack-executing malware ieeexplore.ieee.org
(December 2006)
-
A complexity measure ieeexplore.ieee.org
-
Fileprints: Identifying file types by n-gram analysis ieeexplore.ieee.org
(June 2005)
-
Entropy-driven visualization in gview: Unveiling the unknown in binary file formats ieeexplore.ieee.org
(September 2024) :star:
-
A survey on adversarial attacks for malware analysis ieeexplore.ieee.org
(December 2024) :star:
-
Packed code detection using shannon entropy and homomorphic encrypted executables ieeexplore.ieee.org
(October 2024) :star:
-
Cyclomatic complexity density and software maintenance productivity ieeexplore.ieee.org
-
Watermarking, tamper-proofing, and obfuscation - Tools for software protection ieeexplore.ieee.org
(August 2002)
-
A comparative analysis of classifiers in the recognition of packed executables ieeexplore.ieee.org
(November 2019) :star:
-
Cryptographic function detection in obfuscated binaries via bit-precise symbolic loop mapping ieeexplore.ieee.org
(May 2017)
-
Detecting packed executable file: Supervised or anomaly detection method? ieeexplore.ieee.org
(August 2016)
-
OEPdet ieeexplore.ieee.org
Automated original-entry-point detector.
-
Survey on malware evasion techniques: State of the art and challenges ieeexplore.ieee.org
(February 2012)
-
FatELF: Universal binaries for Linux (HALTED) icculus.org
-
aPLib ibsensoftware.com
Compression library based on the algorithm used in aPACK.
-
Uunp (IDA Pro plugin) hex-rays.com
IDA Pro debugger plug-in module automating the analysis and unpacking of packed binaries.
-
GetTyp helger.com
File format detection program for DOS based on special strings and byte code.
-
PExplorer heaventools.com
Most feature-packed program for inspecting the inner workings of your own software, and more importantly, third party Windows applications and libraries for which you do not have source code.
-
Building high-quality datasets of packed executables - Enhancing static detection models via curated packed binary… hdl.handle.net
(August 2025) :star:
-
Design and implementation of a modular executable packer - Experimenting with packing techniques and static detection hdl.handle.net
(June 2025) :star:
-
Incremental clustering of malware packers using features based on transformed CFG hal.science
(November 2022) :star:
-
Dynamic binary instrumentation for deobfuscation and unpacking hal.inria.fr
(November 2009)
-
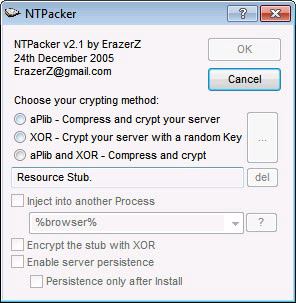
NTPacker hacking-software-free-download.blogspot.com
PE file packer relying on aPlib for compression and/or XOR for encryption.
-
DexGuard guardsquare.com
Android app obfuscation & security protocols for mobile app protection.
-
Implementing your own generic unpacker gsec.hitb.org
-
Binutils gnu.org
The GNU Binutils are a collection of binary tools for Linux (it namely includes Readelf).
-
CauseWay Compressor gitlab.com
DOS EXE compressor.
-
SOREL github.com
Sophos-ReversingLabs 20 Million dataset.
-
Pefeats github.com
Utility for extracting 119 features from a PE file for use with machine learning algorithms.
-
Hyperion github.com
-
MalwareSamples github.com
Bringing you the best of the worst files on the Internet.
-
DIE github.com
Detect It Easy ; Program for determining types of files.
- next page of items loading…