Computer Science
7,622 items in 38 lists
-
skillsaw skillsaw.org
Configurable linter for the files that steer AI coding agents, including skills, plugins, instruction files, hooks, and related configuration. Detects structural, content-quality, and security issues and provides deterministic autofixes, baselines, and CI-ready output.
-
Goodcheck sider.github.io
Regexp based customizable linter.
-
shellcheck shellcheck.net
ShellCheck, a static analysis tool that gives warnings and suggestions for bash/sh shell scripts.
-
Semgrep Supply Chain semgrep.dev
copyright: — Quickly find and remediate high-priority security issues. Semgrep Supply Chain prioritizes the 2% of vulnerabilities that are reachable from your code.
-
StaticReviewer securityreviewer.net
copyright: — Static Reviewer executes code checks according to the most relevant Secure Coding Standards, OWASP, CWE, CVE, CVSS, MISRA, CERT, for 40+ programming languages, using 1000+ built-in validation rules for Security, Deadcode & Best Practices Available a module for…
-
Precaution securesauce.dev
Precaution is a static analysis security tool (SAST) designed to find potentially critical vulnerabilities in source code prior to production. It is available as a CLI, GitHub Action, and GitHub App.
-
gosec (gas) securego.io
Inspects source code for security problems by scanning the Go AST.
-
Understand scitools.com
copyright: — Code visualization tool that provides code analysis, standards testing, metrics, graphing, dependency analysis and more for Ada, VHDL, and others.
-
SAST Online sast.online
copyright: — Check the Android Source code thoroughly to uncover and address potential security concerns and vulnerabilities. Static application security testing (Static Code Analysis) tool Online
-
Safety safetycli.com
Python dependency vulnerability scanner designed to enhance software supply chain security by detecting packages with known vulnerabilities. Checks Python dependencies against a database of known security vulnerabilities and provides detailed reports. Supports CI/CD integration…
-
SafeQL safeql.dev
Validate and auto-generate TypeScript types from raw SQL queries in PostgreSQL. SafeQL is an ESLint plugin for writing SQL queries in a type-safe way.
-
cargo-audit rustsec.org
Audit Cargo.lock for crates with security vulnerabilities reported to the RustSec Advisory Database.
-
clippy rust-lang.github.io
A code linter to catch common mistakes and improve your Rust code.
-
rust-analyzer rust-analyzer.github.io
Supports functionality such as 'goto definition', type inference, symbol search, reformatting, and code completion, and enables renaming and refactorings.
-
flog ruby.sadi.st
Flog reports the most tortured code in an easy to read pain report. The higher the score, the more pain the code is in.
-
flay ruby.sadi.st
Flay analyzes code for structural similarities.
-
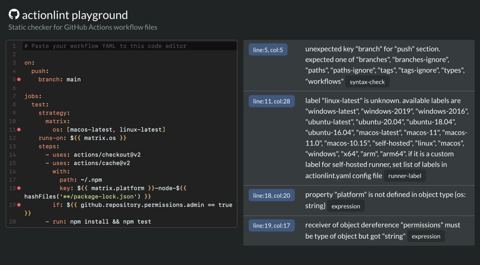
actionlint rhysd.github.io
Static checker for GitHub Actions workflow files. Provides an online version.
-
revive revive.run
Fast, configurable, extensible, flexible, and beautiful linter for Go. Drop-in replacement of golint.
-
retire.js retirejs.github.io
Scanner detecting the use of JavaScript libraries with known vulnerabilities.
-
Repowise repowise.dev
Deterministic, zero-LLM code-health analysis. Scores every file 1-10 for defect risk, maintainability, and performance from 25 markers: McCabe complexity, LCOM4 cohesion, god classes, Rabin-Karp clone detection, change entropy, and untested hotspots. Adds a dependency graph…
-
SwiftLint realm.github.io
A tool to enforce Swift style and conventions.
-
rails_best_practices rails-bestpractices.com
A code metric tool for Rails projects
-
Qwiet AI qwiet.ai
copyright: — Identify vulnerabilities that are unique to your code base before they reach production. Leverages the Code Property Graph (CPG) to run its analyses concurrently in a single graph of graphs. Automatically finds business logic flaws in dev like hardcoded secrets and…
-
qulice qulice.com
Combines a few (pre-configured) static analysis tools (checkstyle, PMD, Findbugs, ...).
-
Qualys Container Security qualys.com
copyright: — Container native application protection to provide visibility and control of containerized applications.
-
pyrefly pyrefly.org
A fast, incremental type checker and language server for Python, providing IDE features like code navigation, semantic highlighting, and code completion.
-
Pysa pyre-check.org
A tool based on Facebook's pyre-check to identify potential security issues in Python code identified with taint analysis.
-
pyre-check pyre-check.org
A fast, scalable type checker for large Python codebases. Pyre-check has been superseded by Pyrefly, its next iteration.
-
fprettify pypi.python.org
Auto-formatter for modern fortran source code, written in Python. Fprettify is a tool that provides consistent whitespace, indentation, and delimiter alignment in code, including the ability to change letter case and handle preprocessor directives, all while preserving revision…
-
pyupgrade pypi.org
A tool (and pre-commit hook) to automatically upgrade syntax for newer versions of the language.
-
pyflakes pypi.org
Check Python source files for errors.
-
mccabe pypi.org
Check McCabe complexity.
-
mbake pypi.org
mbake is a Makefile formatter and linter. It only took 50 years!
-
fixit pypi.org
A framework for creating lint rules and corresponding auto-fixes for source code.
-
autopep8 pypi.org
A tool that automatically formats Python code to conform to the PEP 8 style guide. It uses the pycodestyle utility to determine what parts of the code needs to be formatted.
-
pylint pylint.pycqa.org
Looks for programming errors, helps enforcing a coding standard and sniffs for some code smells. It additionally includes pyreverse (an UML diagram generator) and symilar (a similarities checker).
-
pycodestyle pycodestyle.pycqa.org
(Formerly pep8) Check Python code against some of the style conventions in PEP 8.
-
pyanalyze pyanalyze.readthedocs.io
A tool for programmatically detecting common mistakes in Python code, such as references to undefined variables and type errors. It can be extended to add additional rules and perform checks specific to particular functions.
-
PVS-Studio pvs-studio.com
copyright: — PVS-Studio is a SAST tool that enhances code quality, security, and safety. Supported languages: C, C++, C#, Java, Go, JavaScript and TypeScript. Works on Windows, macOS, Linux. Supports intermodular, incremental, data flow analysis, taint analysis. Provides…
-
Puma Scan pumasecurity.io
Puma Scan provides real time secure code analysis for common vulnerabilities (XSS, SQLi, CSRF, LDAPi, crypto, deserialization, etc.) as development teams write code in Visual Studio.
-
Application Inspector ptsecurity.com
copyright: — Commercial Static Code Analysis which generates exploits to verify vulnerabilities.
-
PT Application Inspector ptsecurity.com
copyright: — Identifies code flaws and detects vulnerabilities to prevent web attacks. Demonstrates remote code execution by presenting possible exploits.
-
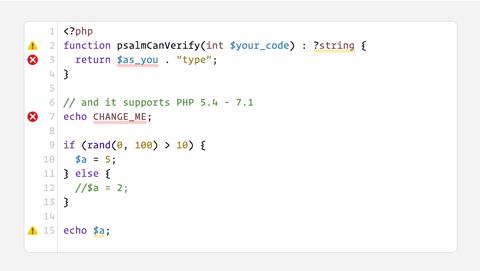
Psalm psalm.dev
Static analysis tool for finding type errors in PHP applications.
-
solhint protofire.github.io
Solhint is an open source project created by https://protofire.io. Its goal is to provide a linting utility for Solidity code.
-
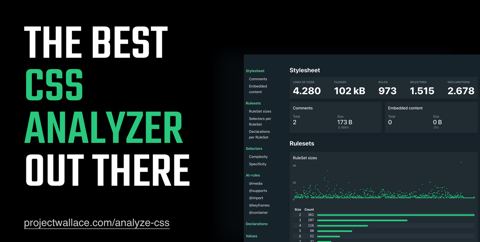
Project Wallace CSS Analyzer projectwallace.com
Analytics for CSS, part of Project Wallace.
-
PMD pmd.github.io
A source code analyzer for Java, Salesforce Apex, Javascript, PLSQL, XML, XSL and others.
-
Php Inspections (EA Extended) plugins.jetbrains.com
A Static Code Analyzer for PHP.
-
Cloud (IaC) Security for JetBrains IDEs plugins.jetbrains.com
Cloud (IaC) Security plugin for JetBrains IDEs. Performs real-time inspections of Docker & Kubernetes IaC with 50+ rules based on Docker image/build security best practices, Kubernetes Pod Security Standards, and NSA/CISA Kubernetes Hardening Guidance.
-
Doop plast-lab.github.io
Doop is a declarative framework for static analysis of Java/Android programs, centered on pointer analysis algorithms. Doop provides a large variety of analyses and also the surrounding scaffolding to run an analysis end-to-end (fact generation, processing, statistics, etc.).
-
test pkg.go.dev
Show location of test failures from the stdlib testing module.
- next page of items loading…