-
UUP sac.sk
Universal exe-file UnPacker.
-
Uundo sac.sk
Universal Undo - Universal Unpacker.
-
UU sac.sk
Universal Unpacker.
-
UPack sac.sk
Compresses Windows PE file.
-
TinyProg sac.sk
EXE and COM programs compressor.
-
SPack sac.sk
-
Shrinker sac.sk
Compresses (up to 70%) 16 and 32 bit Windows and real mode DOS programs.
-
RUPP sac.sk
ROSE SWE UnPaCKER PaCKaGE (for DOS executables only).
-
RTD sac.sk
Rose Patch - TinyProt/Rosetiny Unpacker.
-
RJCrush sac.sk
EXE and COM files compressor with the ability to compress overlays.
-
RERP sac.sk
ROSE's EXE Relocation Packer.
-
RDMC sac.sk
DMC algorithm based packer.
-
LIEF: Library to instrument executable formats romainthomas.fr
-
x86.Virtualizer rewolf.pl
x86 Virtualizer.
-
Titanium Platform reversinglabs.com
Machine learning hybrid cloud platform that harvests thousands of file types at scale, speeds threat detection through machine learning binary analysis, and continuously monitors an index of over 10B files for future threats.
-
Packers/Protectors for Linux reverseengineering.stackexchange.com
-
A compact multi-step framework for packing identification in portable executable files for malware analysis researchsquare.com
(February 2024) :star:
-
A fast randomness test that preserves local detail researchrepository.rmit.edu.au
(October 2008)
-
Advanced feature engineering for static detection of executable packing researchportal.rma.ac.be
(June 2024) :star:
-
Generic packing detection using several complexity analysis for accurate malware detection researchgate.net
(January 2014)
-
A comparative analysis of software protection schemes researchgate.net
(June 2014)
-
Pandora's Bochs: Automatic unpacking of malware researchgate.net
(January 2008)
-
Runtime Packers Testset researchgate.net
Dataset of 10 common Malware files, packed with about 40 different runtime packers in over 500 versions and options, with a total of about 5,000 samples.
-
Toward generic unpacking techniques for malware analysis with quantification of code revelation researchgate.net
(August 2009)
-
Deobfuscation of packed and virtualization-obfuscation protected binaries repository.arizona.edu
(June 2011)
-
Unpacking framework for packed malicious executables repositorio-aberto.up.pt
(July 2013)
-
Robust static analysis of portable executable malware repo.zenk-security.com
(December 2014)
-
Executable and linking format (ELF) specification refspecs.linuxfoundation.org
-
Mach-O - A look at apple executable files redmaple.tech
-
PackHero: A scalable graph-based approach for efficient packer identification re.public.polimi.it
(July 2025) :star:
-
ProTools protools.narod.ru
Programmer's Tools, a web site dedicated for all kinds of tools and utilities for the true WinBloze programmer, including packers, crypters, etc.
-
CryptExec phrack.org
Next-generation runtime binary encryption using on-demand function extraction.
-
-
Anti-unpacker tricks pferrie.tripod.com
-
Standards and policies on packer use pferrie.epizy.com
-
The "Ultimate" anti-debugging reference pferrie.epizy.com
-
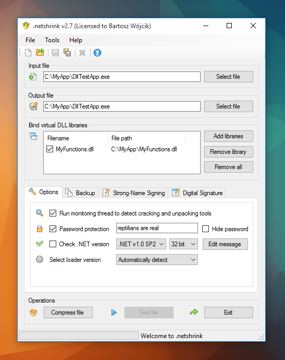
.netshrink pelock.com
Executable compressor for your Windows or Linux .NET application executable file using LZMA.
-
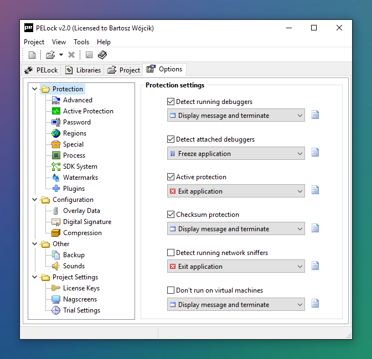
PELock pelock.com
Software protection system for Windows executable files ; protects your applications from tampering and reverse engineering, and provides extensive support for software license key management, including support for time trial periods.
-
PEdump pedump.me
Dump windows PE files using Ruby.
-
PCjs pcjs.org
Uses JavaScript to recreate the IBM PC experience, using original ROMs, CPUs running at their original speeds, and early IBM video cards and monitors.
-
Shiva packetstormsecurity.com
Tool to encrypt ELF executables under Linux.
-
cryptelf packetstormsecurity.com
Modifies binary by appending code to handle runtime decryption, changing the program EP and changing the .note segment to LOAD ; encrypts the .text section by XORing its bytes with a key.
-
BurnEye packetstormsecurity.com
ELF encryption program, x86-linux binary.
-
-
-
Themida oreans.com
From Renovo paper: Themida converts the original x86 instructions into virtual instructions in its own randomized instruction set, and then interpret these virtual instructions at run-time.
-
Code Virtualizer oreans.com
Powerful code obfuscation system for Windows, Linux and macOS applications that helps developers to protect their sensitive code areas against Reverse Engineering with very strong obfuscation code, based on code virtualization.
-
UnThemida: Commercial obfuscation technique analysis with a fully obfuscated program onlinelibrary.wiley.com
(July 2018) :star:
-
Improving malware detection using multi-view ensemble learning onlinelibrary.wiley.com
(August 2016) :star:
-
Packer identification method based on byte sequences onlinelibrary.wiley.com
(November 2018)
- next page of items loading…