-
All-in-one framework for detection, unpacking, and verification for malware analysis onlinelibrary.wiley.com
(January 2019) :star:
-
Classification of malware by using structural entropy on convolutional neural networks ojs.aaai.org
(April 2018)
-
Obsidium obsidium.de
Feature-rich professional software protection and licensing system designed as a cost effective and easy to implement, yet reliable and non-invasive way to protect your 32- and 64-bit Windows software applications and games from reverse engineering.
-
CFF Explorer ntcore.com
PE32/64 and .NET editor, part of the Explorer Suite.
-
PE Detective ntcore.com
This GUI tool can scan single PE files or entire directories (also recursevely) and generate complete reports.
-
NSPack nspack.apponic.com
32/64-bits exe, dll, ocx, scr Windows program compressor.
-
When malware is packin' heat; limits of machine learning classifiers based on static analysis features ndss-symposium.org
(January 2020) :star: :star:
-
Prevalence and impact of low-entropy packing schemes in the malware ecosystem ndss-symposium.org
(February 2020) :star:
-
Things you may not know about Android (Un) packers: A systematic study based on whole-system emulation. ndss-symposium.org
(February 2018)
-
Entropy and the distinctive signs of packer PE files n10info.blogspot.com
-
-
Unpacking the potential of "Packing box" medium.com
-
TitanMist: Your first step to reversing nirvana media.blackhat.com
-
An improved method for packed malware detection using PE header and section table information mecs-press.org
(September 2019)
-
Identifying malware packers through multilayer feature engineering in static analysis mdpi.com
(February 2024) :star:
-
Bypassing heaven’s gate technique using black-box testing mdpi.com
(November 2023) :star:
-
Mimicking anti-viruses with machine learning and entropy profiles mdpi.com
(2019-05-21)
-
Packer detection for multi-layer executables using entropy analysis mdpi.com
(March 2017) :star:
-
Packed malware variants detection using deep belief networks matec-conferences.org
(March 2020)
-
MRC mandiant-red-curtain.apponic.com
(Mandiant Red Curtain) Free software for Incident Responders that assists with the analysis of malware ; it examines executable files (e.g., .exe, .dll, and so on) to determine how suspicious they are based on a set of criteria.
-
MalwareTips malwaretips.com
Community-driven platform providing the latest information and resources on malware and cyber threats.
-
MalwareGallery malwaregallery.com
Yet another malware collection in the Internet.
-
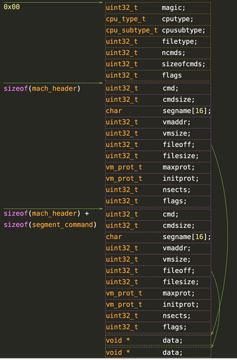
Parsing mach-O files lowlevelbits.org
-
Squishy logicoma.io
Modern packer developed for 64kb demoscene productions, targets 32bit and 64bit executables.
-
Wavelet decomposition of software entropy reveals symptoms of malicious code linkinghub.elsevier.com
(December 2016)
-
Performance evaluation of filter-based feature selection techniques in classifying portable executable files linkinghub.elsevier.com
(January 2018) :star:
-
Conceptual and empirical comparison of dimensionality reduction algorithms (PCA, KPCA, LDA, MDS, SVD, LLE, ISOMAP, LE… linkinghub.elsevier.com
(May 2021)
-
API-MalDetect: Automated malware detection framework for windows based on API calls and deep learning techniques linkinghub.elsevier.com
(September 2023) :star:
-
G3MD: Mining frequent opcode sub-graphs for metamorphic malware detection of existing families linkinghub.elsevier.com
(December 2018)
-
Metamorphic malware identification using engine-specific patterns based on co-opcode graphs linkinghub.elsevier.com
(August 2020) :star:
-
Benchmark for filter methods for feature selection in high-dimensional classification data linkinghub.elsevier.com
(March 2020) :star:
-
Resurrecting anti-virtualization and anti-debugging: Unhooking your hooks linkinghub.elsevier.com
(March 2021) :star:
-
Beyond the sandbox: Leveraging symbolic execution for evasive malware classification linkinghub.elsevier.com
(February 2025) :star:
-
Adversarial attacks against Windows PE malware detection: A survey of the state-of-the-art linkinghub.elsevier.com
(May 2023) :star:
-
A systematical and longitudinal study of evasive behaviors in windows malware linkinghub.elsevier.com
(February 2022) :star:
-
A novel framework for image-based malware detection with a deep neural network linkinghub.elsevier.com
(October 2021) :star:
-
Auditing static machine learning anti-Malware tools against metamorphic attacks linkinghub.elsevier.com
(March 2021) :star:
-
A framework for metamorphic malware analysis and real-time detection linkinghub.elsevier.com
(February 2015)
-
Opcode sequences as representation of executables for data-mining-based unknown malware detection linkinghub.elsevier.com
(May 2013) :star:
-
Research of software information hiding algorithm based on packing technology link.springer.com
(September 2020)
-
Generic unpacking method based on detecting original entry point link.springer.com
(November 2013)
-
Detecting traditional packers, decisively link.springer.com
(October 2013)
-
A static, packer-agnostic filter to detect similar malware samples link.springer.com
(July 2012)
-
A fine-grained classification approach for the packed malicious code link.springer.com
(October 2012)
-
OPEM: A static-dynamic approach for machine-learning-based malware detection link.springer.com
(September 2012)
-
PEAL - Packed executable analysis link.springer.com
(January 2012)
-
Semi-supervised learning for unknown malware detection link.springer.com
(April 2011)
-
Pattern recognition techniques for the classification of malware packers link.springer.com
(July 2010)
-
Denial-of-service attacks on host-based generic unpackers link.springer.com
(December 2009)
-
PE-Miner: Mining structural information to detect malicious executables in realtime link.springer.com
(September 2009)
- next page of items loading…