-
BitBlaze bitblaze.cs.berkeley.edu
Analysis platform that features a novel fusion of static and dynamic analysis techniques, mixed concrete and symbolic execution, and whole-system emulation and binary instrumentation, all to facilitate state-of-the art research on real security problems.
-
MalwareBazaar bazaar.abuse.ch
Project operated by abuse.ch aimed to collect and share malware samples, helping IT-security researchers and threat analysts protecting their constituency and customers from cyber threats.
-
Runtime packers testing experiences av-test.org
-
AutoIT autoitscript.com
Legitimate executable encryption service.
-
BIN-crypter autoitscript.com
EXE protection software against crackers and decompilers.
-
MPRESS autohotkey.com
Compresses (using LZMA) and protects PE, .NET or Mach-O programs against reverse engineering.
-
-
-
ASProtect 64 aspack.com
Tool for protecting 64-bit applications and .NET applications for Windows against unauthorized use, industrial and home copying, professional hacking and analysis of software products distributed over the Internet and on any physical media.
-
ASProtect 32 aspack.com
Multifunctional EXE packing tool designed for software developers to protect 32-bit applications with in-built application copy protection system.
-
ASPack aspack.com
Advanced solution created to provide Win32 EXE file packing and to protect them against non-professional reverse engineering.
-
On deceiving malware classification with section injection arxiv.org
(August 2022) :star:
-
Practical attacks on machine learning: A case study on adversarial windows malware arxiv.org
(September 2022) :star:
-
Longitudinal study of the prevalence of malware evasive techniques arxiv.org
(December 2021) :star:
-
Transcending transcend: Revisiting malware classification in the presence of concept drift arxiv.org
(December 2021) :star:
-
MAB-Malware: A reinforcement learning framework for attacking static malware classifiers arxiv.org
(April 2021) :star:
-
Malware makeover: Breaking ML-based static analysis by modifying executable bytes arxiv.org
(May 2021) :star:
-
Intriguing properties of adversarial ML attacks in the problem space arxiv.org
(March 2020) :star:
-
On evaluating adversarial robustness arxiv.org
(February 2019) :star:
-
-
On the worst-case complexity of timsort arxiv.org
-
EMBER: An open dataset for training static PE malware machine learning models arxiv.org
(April 2018) :star: :star:
-
Deceiving end-to-end deep learning malware detectors using adversarial examples arxiv.org
(January 2019) :star:
-
Learning to evade static PE machine learning malware models via reinforcement learning arxiv.org
(January 2018) :star:
-
Malware analysis using multiple API sequence mining control flow graph arxiv.org
(July 2017)
-
Generating adversarial malware examples for black-box attacks based on GAN arxiv.org
(February 2020) :star:
-
Technical report on the cleverhans v2.1.0 adversarial examples library arxiv.org
(June 2018) :star:
-
Novel feature extraction, selection and fusion for effective malware family classification arxiv.org
(March 2016)
-
-
Intriguing properties of neural networks arxiv.org
(February 2014)
-
Generic unpacking of self-modifying, aggressive, packed binary programs arxiv.org
(May 2009)
-
A heuristics-based static analysis approach for detecting packed PE binaries article.nadiapub.com
(October 2013)
-
Anti debugging protection techniques with examples apriorit.com
-
Malware detection through opcode sequence analysis using machine learning api.semanticscholar.org
(June 2015)
-
Source-free binary mutation for offense and defense api.semanticscholar.org
(December 2014)
-
About anti-debug tricks anti-debug.checkpoint.com
-
ResourceHacker angusj.com
Resource editor for 32bit and 64bit Windows applications.
-
SymPack amazon.com
Safe, portable, largely effective but not generic library for packing detection and unpacking ; part of the Norton Antivirus solution.
-
Alternate EXE Packer alternate-tools.com
Compression tool for executable files (type EXE) or DLL's relying on UPX 3.96.
-
Alienyze alienyze.com
Advanced software protection and security for Windows 32-bit executables.
-
LordPE aldeid.com
PE header viewer, editor and rebuilder.
-
ImpREC aldeid.com
This can be used to repair the import table for packed programs.
-
Efficient automatic original entry point detection airitilibrary.com
(January 2019)
-
An efficient algorithm to extract control flow-based features for ioT malware detection academic.oup.com
(April 2021) :star:
-
20to4 20to4.net
Executable compressor that is able to stuff about 20k of finest code and data into less than 4k.
-
Dealing with virtualization packers 2008.caro.org
-
Pandora's Bochs 0x0badc0.de
Extension to the Bochs PC eumlator to enable it to monitor execution of the unpacking stubs for extracting the original code.
-
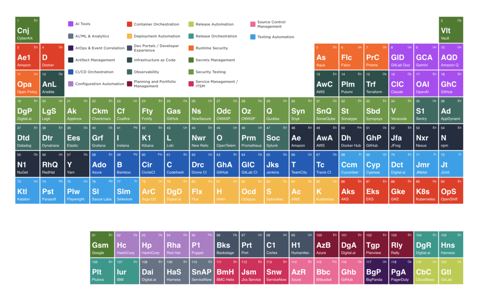
Periodic Table of DevOps Tools xebialabs.com
XebiaLabs - A collection of DevSecOps tooling categorised by tool functionality.
-
Alice and Bob Learn Application Security wiley.com
Tanya Janca - An accessible and thorough resource for anyone seeking to incorporate, from the beginning of the System Development Life Cycle, best security practices in software development.
-
Coding Standards wiki.sei.cmu.edu
CERT - A collection of secure development standards for C, C++, Java and Android development.
- next page of items loading…