-
CVE-2017-2446 or JSC::JSGlobalObject::isHavingABadTime. doar-e.github.io
-
DFIR ORC dfir-orc.github.io
DFIR ORC is a collection of specialized tools dedicated to reliably parse and collect critical artifacts such as the MFT, registry hives or event logs. DFIR ORC collects data, but does not analyze it: it is not meant to triage machines. It provides a forensically relevant…
-
-
Scrutiny datarift.blogspot.tw
-
Dark Reading darkreading.com
-
XSS via a spoofed React element danlec.com
-
Cyber Triage cybertriage.com
Cyber Triage collects and analyzes host data to determine if it is compromised. It's scoring system and recommendation engine allow you to quickly focus on the important artifacts. It can import data from its collection tool, disk images, and other collectors (such as KAPE). It…
-
csp evaluator csper.io
-
Csper csper.io
-
Laravel CSP Generator csp-generator.shakiltech.com
-
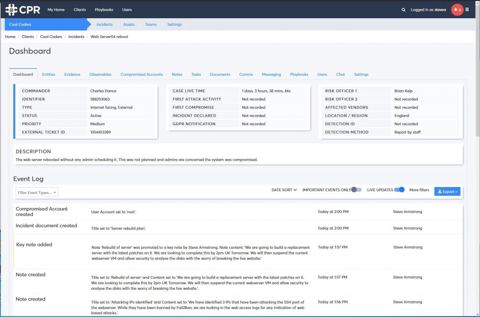
CyberCPR cybercpr.com
Community and commercial incident management tool with Need-to-Know built in to support GDPR compliance while handling sensitive incidents.
-
What is a Side-Channel Attack ? csoonline.com
-
Certificate Search crt.sh
-
ARTist artist.cispa.saarland
a flexible open-source instrumentation and hybrid analysis framework for Android apps and Android's Java middleware. It is based on the Android Runtime's (ART) compiler and modifies code during on-device compilation.
-
CrowdSec crowdsec.net
-
Crowd Response crowdstrike.com
Lightweight Windows console application designed to aid in the gathering of system information for incident response and security engagements. It features numerous modules and output formats.
-
AppSweep by Guardsquare appsweep.guardsquare.com
Free, fast Android application security testing for developers
-
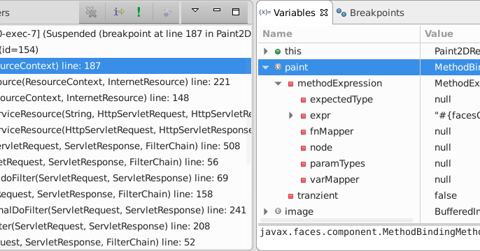
Poor RichFaces codewhitesec.blogspot.com
-
AppUse appsec-labs.com
custom build for penetration testing
-
Censys censys.io
-
Computer Aided Investigative Environment (CAINE) caine-live.net
Contains numerous tools that help investigators during their analysis, including forensic evidence collection.
-
How we exploited a remote code execution vulnerability in math.js capacitorset.github.io
-
Live Response Collection brimorlabs.com
Automated tool that collects volatile data from Windows, OSX, and *nix based operating systems.
-
-
IBM Security AppScan Mobile Analyzer appscan.bluemix.net
not free
-
BRETT BUERHAUS buer.haus
-
grayhatwarfare buckets.grayhatwarfare.com
-
Broken Browser brokenbrowser.com
-
IREC binalyze.com
All-in-one IR Evidence Collector which captures RAM Image, $MFT, EventLogs, WMI Scripts, Registry Hives, System Restore Points and much more. It is FREE, lightning fast and easy to use.
-
approver approver.talos-sec.com
Approver is a fully automated security analysis and risk assessment platform for Android and iOS apps. Not free.
-
Appknox appknox.com
not free
-
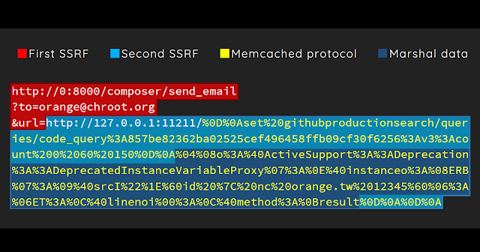
GitHub Enterprise Remote Code Execution bounty.github.com
-
-
App Detonator appdetonator.run
Detonate APK binary to provide source code-level details, including app author, signature, build, and manifest information. 3 Analysis/day free quota.
-
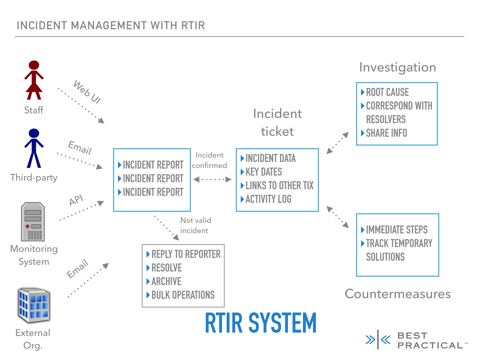
RTIR bestpractical.com
Request Tracker for Incident Response (RTIR) is the premier open source incident handling system targeted for computer security teams. We worked with over a dozen CERT and CSIRT teams around the world to help you handle the ever-increasing volume of incident reports. RTIR…
-
-
AppCritique appcritique.boozallen.com
Upload your Android APKs and receive comprehensive free security assessments
-
SSD Advisory – Chrome Turbofan Remote Code Execution blogs.securiteam.com
-
Taintdroid appanalysis.org
requires AOSP compilation
-
Laravel Content Security Policy: Complete Implementation Guide blog.shakiltech.com
-
Fraunhofer App-ray app-ray.co
expired domain
-
Belkasoft Live RAM Capturer belkasoft.com
Tiny free forensic tool to reliably extract the entire content of the computer’s volatile memory – even if protected by an active anti-debugging or anti-dumping system.
-
Remote Code Execution on a Facebook server blog.scrt.ch
-
NVISO ApkScan apkscan.nviso.be
sunsetting on Oct 31, 2019
-
A Methodical Approach to Browser Exploitation blog.ret2.io
-
Belkasoft Evidence Center belkasoft.com
The toolkit will quickly extract digital evidence from multiple sources by analyzing hard drives, drive images, memory dumps, iOS, Blackberry and Android backups, UFED, JTAG and chip-off dumps.
-
-
Apkpure apkpure.com
Online apk downloader. Also, it provides its own app for downloading.
-
GitHub Enterprise SQL Injection blog.orange.tw
-
APK Downloader apkcombo.com
Online Service to download APK from the Play Store for a specific Android Device Configuration
- next page of items loading…